Risk ManagementPast programme

Turning Third-Party Risk Management into an Intelligence Operation

Wednesday 20 May 2026 • 12:00 • Dallas

About the evening

For security leaders, third-party risk is no longer a compliance problem — it is a business risk that can disrupt operations, expose sensitive data, and erode trust. Yet many programs still rely on point-in-time assessments and static risk indicators that fail to reflect real-world threats. This roundtable discussion explores how security leaders are reframing third-party risk management as an intelligence operation, using real-time information, continuous monitoring, and threat intelligence to identify and act on material risk across the digital supply chain.
Guest feedback

What the room said.

From the feedback forms guests filled in at the end of the evening.

9.5/10average guest rating
100%asked Mastercard for a next step
13guests gave feedback
“The discussion was robust, with a great cross section of executives that provided wide-ranging viewpoints and excellent insight. I left with more information about the subject than when I came.”
AVP Global Infrastructure ServicesGM Financial
“A great discussion given the smaller group. Excellent facilitation.”
Senior Director, Cybersecurity ComplianceWPP Media
Around the table

13 organisations took a seat.

Company names only. What was said at the table stays under the Chatham House Rule.

  • AT&T
  • Caterpillar
  • Charles Schwab
  • Colliers Group
  • DTCC
  • GM Financial
  • HP
  • Lockheed Martin
  • Securonix
  • Solis Mammography
  • Stitch Fix
  • Taylor Corporation
  • WPP Media
In the room

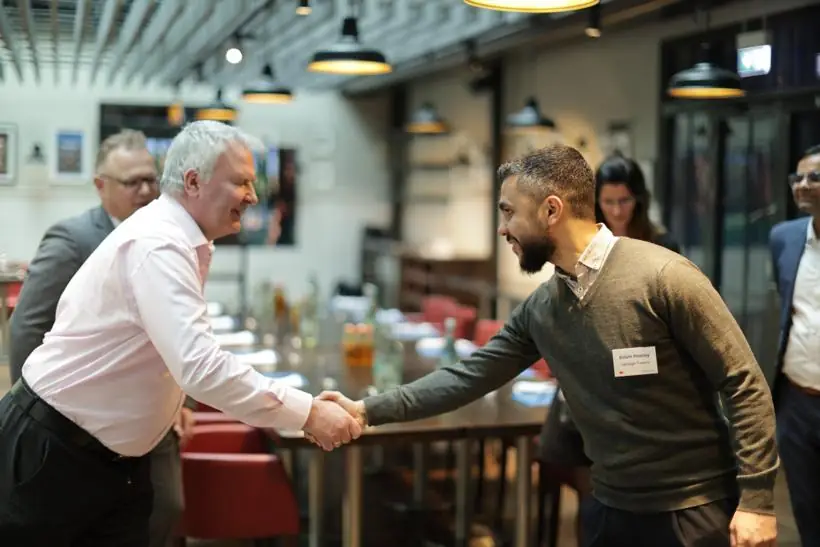
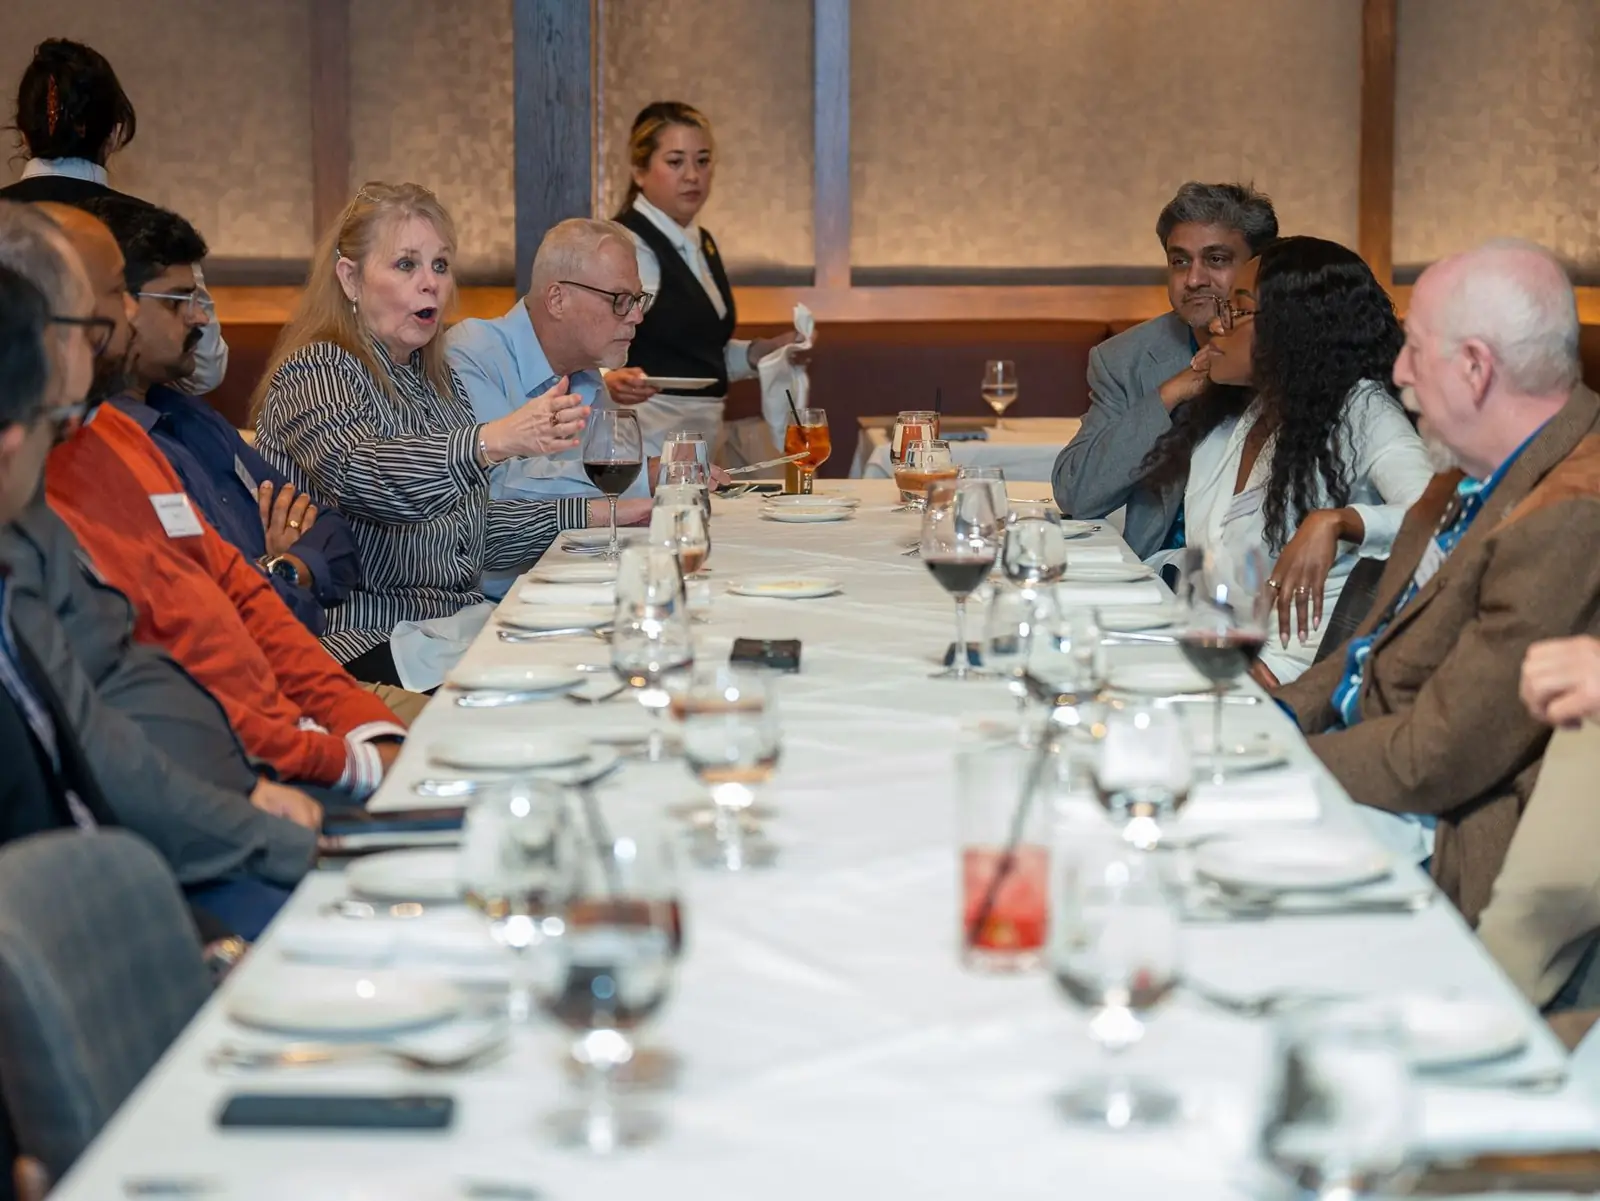
Photographs from the evening.

See the full portfolio →